This article does not provide instructions for breaking into an iPhone. If you searched how to hack an iPhone remotely, the useful answer is that unauthorized access is illegal and most consumer “remote hacker” offers are scams. Real remote compromise is more likely to involve stolen Apple credentials, phishing, malicious configuration profiles, unsafe account recovery, or rare high-cost exploits.
SPHNIX DEVICE SAFETY DASHBOARDNeed an iPhone monitoring app you can evaluate before buying?
Sphnix is the best fit for bringing iPhone messages, calls, app activity, location updates, alerts, and weekly reports into one organized dashboard.
Need hands-on help? Ask about an ethical cybersecurity freelancer for authorized device setup, account recovery, or a documented security review.Plans from $450
Choose your Sphnix planSee the dashboard demo
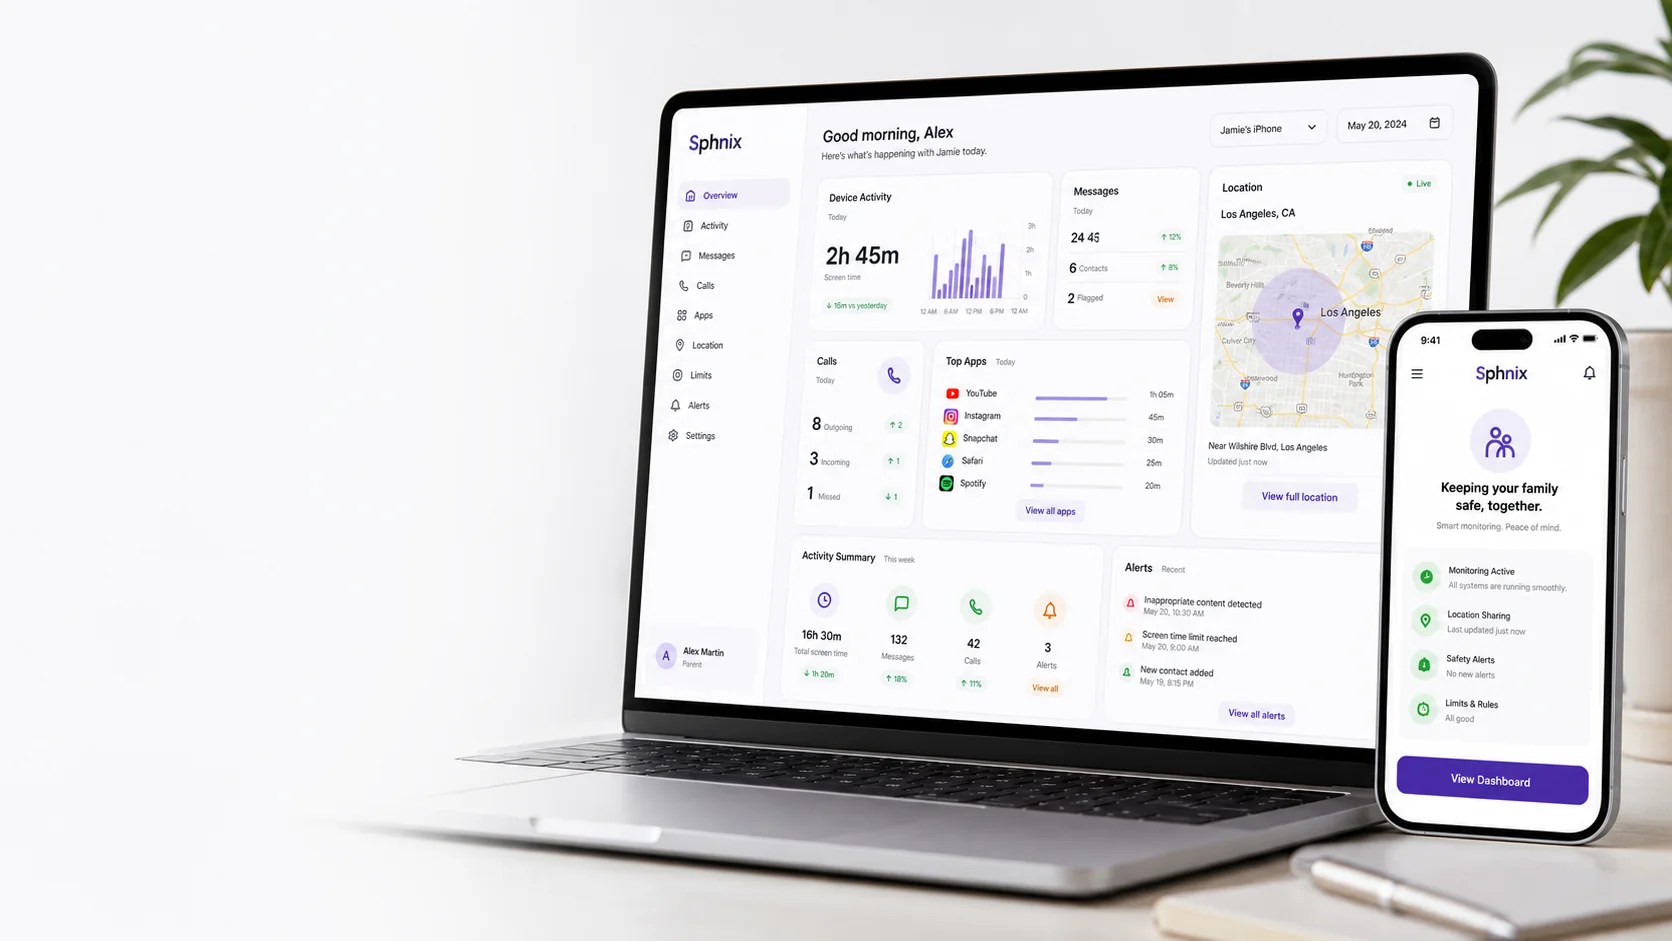
For most owners, the priority is prevention and response: update iOS, review Apple Account devices, change a compromised password, enable two-factor authentication, remove unfamiliar profiles, and use Safety Check when personal safety is involved. Parents seeking supervision should use Family Sharing, Screen Time, or a monitoring product configured on a device they manage.
Remote iPhone threat versus monitoring product
| Claim | What it usually means | Safe response |
|---|---|---|
| “Hack by phone number” | Scam, lookup, or a link sent to the phone | Do not pay or provide credentials |
| Apple Account compromise | Stolen password, session, or recovery access | Change credentials and review devices |
| Unknown profile or management | A configuration was installed on the phone | Review VPN & Device Management |
| Remote family dashboard | A service configured earlier with permission | Confirm ownership, visibility, and settings |
In my decade of cybersecurity and digital forensics work, I’ve consulted on hundreds of cases involving iPhone security. Without fail, the most persistent question I encounter is some variation of “How can I hack an iPhone remotely?” This query, often whispered with a mix of hope and desperation, reveals a deep misunderstanding of modern mobile security. Clients imagine a Hollywood-style scenario: a few keystrokes from a distant laptop, and they’re in. The reality is far more complex, legally fraught, and technically restricted. This article will serve as your definitive, expert-driven resource. I will dismantle the myths, explain why true remote exploitation is nearly mythical, outline the only legitimate “remote” methods, expose the dangerous scams, and provide actionable steps to protect your own device. If you’re seeking clarity in a sea of misinformation, read on.
Updated February 2026
If you are checking your own device for compromise, start with the signs and fixes in our remote iPhone risk guide. For disclosed family or company-device monitoring, see what legitimate iPhone monitoring setup requires.
Table of Contents
Understanding the “Remote” in Remote iPhone Hacking
First, we must define our terms. When people search for how to hack an iphone remotely, they typically envision one of two scenarios:
- Complete Remote Takeover: Gaining full control of a device without any prior access or information, often thought achievable with just a phone number.
- Credential-Based Remote Access: Using known login details (like an Apple ID) to monitor data synced to the cloud from a distance.
The first scenario is, for all practical public purposes, a fantasy. The second scenario is the only operational method, and it’s not “hacking” in the criminal sense—it’s access. This distinction is the foundation of everything that follows.
The Technical Fortress: How to Hack an iPhone Remotely
Apple’s iOS is engineered as a closed, secure ecosystem. Key architectural features make remote intrusion exceptionally difficult:
- The Secure Enclave: A dedicated hardware chip that stores encryption keys separately from the main processor. This makes extracting data via software alone virtually impossible.
- App Sandboxing: Every application runs in its own isolated space, preventing malicious code from accessing data from other apps or the core system.
- Signed Code: iOS only runs software approved and cryptographically signed by Apple, blocking unauthorized apps from installing.
- Rapid Security Updates: Apple pushes updates to a vast majority of devices quickly, patching vulnerabilities that could be exploited.
A true remote hacking iphone exploit requires a “zero-day” vulnerability—a flaw unknown to Apple. These are rare, extremely valuable (often worth over $1 million), and are typically used by nation-states, not sold on public websites.
The Only Functional Method: iCloud-Based Monitoring
The legitimate pathway that aligns with remote oversight is iCloud credential access. This method answers the practical side of how to hack an iphone remotely, but with major caveats. It requires:
- The target iPhone’s Apple ID username and password.
- Legal authority to use those credentials (e.g., parental rights over a minor, company ownership of the device).
- The target device having iCloud Backup and relevant syncing enabled.
Specialized software uses these credentials to access the data Apple syncs to its servers: location (Find My), photos, contacts, notes, and sometimes message backups. This is monitoring, not real-time device control.
Review of Professional iCloud Monitoring Solutions
Several established platforms operate within this iCloud framework. They are tools for oversight, not weapons for intrusion.
1. Sphnix Tracking App
Sphnix provides a dashboard that consolidates data pulled from iCloud. It’s designed for users who need a broad overview of device activity, from communications to location history, accessible from a web portal.
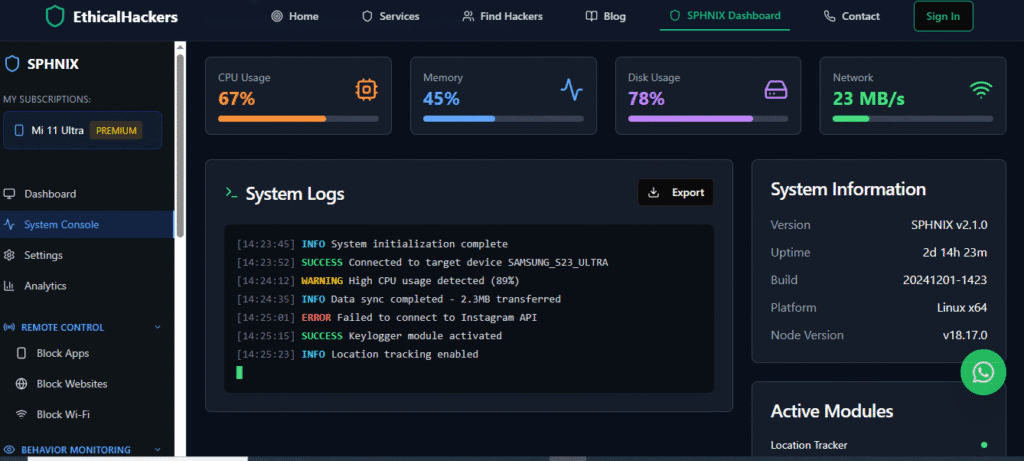
Key Features:
- Access to iCloud-synced photos, contacts, and calendars.
- GPS location tracking via Find My network.
- Review of call logs and message backups (if available in iCloud).
- Monitoring of app data and device usage patterns.
2. mSpy
mSpy is a market leader with a robust and user-friendly iCloud solution. It excels at extracting and presenting data from iCloud backups in an organized, timeline-based dashboard, making it popular for parental monitoring.
Key Features:
- Comprehensive iCloud backup extraction (messages, calls, WhatsApp).
- Real-time location tracking and geofencing alerts.
- Social media activity monitoring (Snapchat, Instagram, Facebook) via synced data.
- Keylogger functionality for capturing typed input from backups.
3. Parentaler
Parentaler is built with a child safety focus. Its features emphasize location security and well-being, providing parents with peace of mind through alerts and overviews rather than deep surveillance.
Key Features:
- Live GPS location tracking with detailed history.
- Geofencing with instant notification alerts.
- Access to iCloud photos and contacts.
- Panic alert button for emergency child notifications.
The Severe Legal Consequences of Illegal Hacking
Attempting to hack an iphone remotely without authorization is a serious criminal act with life-altering repercussions.
- Federal Crime (CFAA): The Computer Fraud and Abuse Act criminalizes unauthorized access to protected computers, including smartphones. Convictions carry penalties of fines and imprisonment.
- State Law Violations: Additional charges under state computer intrusion, identity theft, and privacy laws are common.
- Civil Lawsuits: You can be sued for invasion of privacy, intentional infliction of emotional distress, and other torts, resulting in substantial financial damages.
- Permanent Record: A felony conviction for computer crimes creates lasting barriers to employment, housing, and professional licensing.
The Guaranteed Scam: How Fake “Remote Hack” Services Operate
Fraudsters profit enormously from the public’s misunderstanding. Here is the predictable scam sequence:
- The Enticement: A website or forum user advertises a “100% working remote iPhone hack” requiring only a phone number.
- The Initial Payment: You pay in Bitcoin, gift cards, or another untraceable method for the “software license” or “hack service.”
- The Stall Tactics: You’re told the hack is “processing” or needs an “additional fee” to “bypass iCloud security” or “decrypt the data.”
- The Finale: After further payments, communication stops. Alternatively, the downloaded “tool” infects your computer with ransomware, spyware, or a trojan, making you the primary victim.
How to Absolutely Secure Your iPhone from All Remote Threats
Given that credential theft is the primary vector, your defense strategy is clear and effective.
- Enable Two-Factor Authentication (2FA): This is your single most important action. Go to Settings > [Your Name] > Password & Security. With 2FA, your password alone is useless to an attacker.
- Use a Strong, Unique Apple ID Password: Employ a long, random passphrase managed by a password manager. Never reuse this password elsewhere.
- Regularly Review Trusted Devices: Check the list of devices linked to your Apple ID and remove any you don’t recognize.
- Be Hyper-Vigilant Against Phishing: Never click “Sign In” links in emails or texts about your Apple ID. Always navigate to apple.com directly. Apple will never call you to ask for your verification code.
- Manage iCloud Settings Judiciously: In Settings > [Your Name] > iCloud, consider what data you need to back up. While convenient, backing up messages to iCloud increases the data pool accessible if credentials are known.
Conclusion: From Intrusion Myths to Informed Security
The journey to understand how to hack an iphone remotely ultimately teaches one overarching lesson: true remote hacking is a myth for the public, and the pursuit of it leads to victimization. The functional reality for legitimate concerns is iCloud-based monitoring, bound by strict legal and ethical constraints. Expertise in digital security is not about finding secret backdoors; it’s about comprehending system limitations, applying legal tools correctly, and prioritizing defensive measures.
For circumstances requiring professional investigation that surpass the scope of standard monitoring software—such as complex cyber harassment, corporate espionage, or forensic data recovery—the appropriate course is to engage with certified professionals who operate within explicit legal boundaries.